What security pillars govern enterprise Copilot workflow integration?
Securing enterprise Copilot workflow integration projects requires building a defense-in-depth architecture centered on zero-trust access, data isolation, and comprehensive audit logging. Security teams must ensure that AI assistants process data strictly within isolated tenant boundaries, preventing proprietary corporate data from leaking into public training sets.
Every query processed by the system must undergo automated permission checks to confirm that the user possesses valid authorization credentials for the underlying records.
Enforcing strict tenant isolation guarantees that corporate data remains completely protected against external cross-tenant leakage.
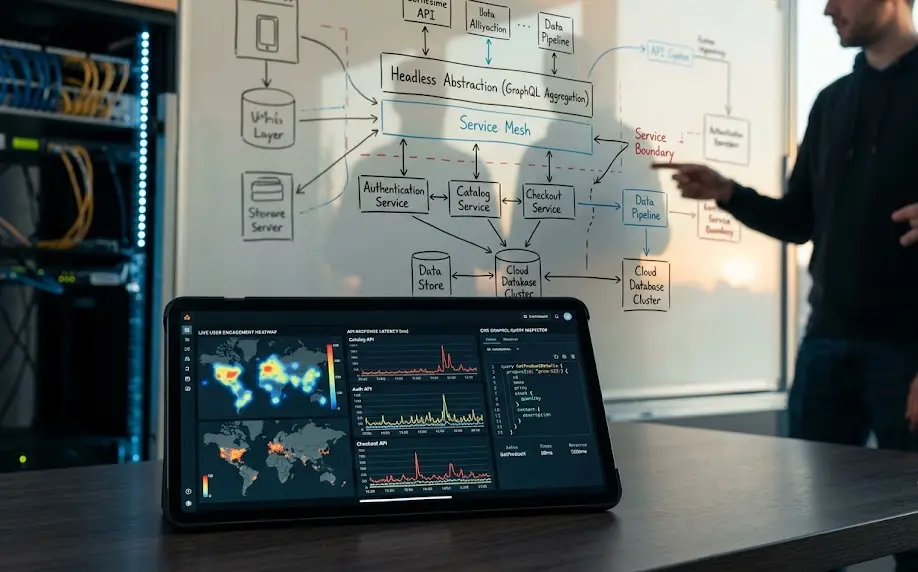
Security controls must be embedded directly into the API integration layer rather than applied as an afterthought.
How does role-based access control prevent internal data exposure?
Role-based access control (RBAC) ensures that AI assistants inherit the exact security permissions assigned to the active user executing a query. If an organization maintains loose file permissions on internal network drives, an integrated assistant might surface executive salary spreadsheets or strategic merger plans during routine employee searches.
Auditing and tightening legacy file permission structures before enabling AI indexing services prevents accidental internal data exposure.
RBAC enforcement provides critical protection across key security vectors:
- Granular file access: Restricting document indexing based on explicit user group memberships and security tags.
- API endpoint scoping: Limiting automated tool-calling functions to authorized administrative roles.
- Database row-level security: Filtering SQL query responses based on user departmental clearance levels.
Why are data loss prevention rules vital for cloud tenants?
Data loss prevention (DLP) policies scan incoming prompts and outgoing model responses for sensitive patterns, such as credit card numbers, social security records, and proprietary source code snippets. When an integrated assistant processes an enterprise workflow, DLP filters intercept prohibited data transfers instantly, preventing policy violations.
Deploying automated sensitivity labeling ensures that confidential corporate documents are excluded from AI vector indexing pipelines.
Analyzing an enterprise Copilot workflow deployment reveals that DLP rules prevent up to ninety percent of accidental data exposure events.
Automated DLP filters act as an essential firewall protecting sensitive data assets in real time.
How do encryption protocols protect data in transit and at rest?
Protecting enterprise communication channels requires applying advanced cryptographic standards across all vector databases, API gateways, and model endpoints. Data in transit between user interfaces and backend AI services must be encrypted using TLS 1.3, while data stored in vector indexes requires AES-256 encryption.
Using dedicated Hardware Security Modules (HSM) to manage encryption keys ensures that corporate entities retain sole control over data decryption capabilities.
Rigorous cryptographic protocols ensure data sovereignty across public, private, and hybrid cloud infrastructures.
What audit strategies ensure compliant enterprise Copilot workflow integration?
Maintaining compliance with standards like SOC 2, ISO 27001, and GDPR demands continuous logging and auditing of all AI assistant interactions. IT administrators must configure automated logging tools that record user identities, prompt timestamps, accessed database endpoints, and model response hashes for security review.
Conducting periodic penetration testing and prompt injection vulnerability scans identifies potential security gaps before malicious actors exploit them.
Implementing a comprehensive security strategy ensures that enterprise Copilot workflow integration remains fully compliant, resilient, and safe. Protecting corporate data assets creates a trusted foundation for continuous software automation across the enterprise.